 SFTPPlus
Security Policies#
Introduction#
A security-policy represents a set of security-related configurations that are applied for the file transfer services.
This section describes the configuration options used to define security policies.
Multiple security policies can be created inside the SFTPPlus configuration.
File transfer services can use the default security policy or can be configured to use a specific security policy.
Warning
Do not configure source IP blocking, if SFTPPlus is behind a Proxy/Gateway or any other network device which does not preserve the source IP address of the initial authentication request or does not support Proxy Protocol v2.
When SFTPPlus is behind a load balancer, make sure that Proxy Protocol version 2 is enabled on the load balancer. Otherwise all the authentication requests will be made using the load balancer's own IP address and not the client IP address.
Check that your network is not vulnerable to IP address spoofing.
Default security policy#
The DEFAULT-SECURITY-POLICY is always present in any SFTPPlus configuration, and it can't be removed. This is used by default by any file transfer service that is not configured with a specific security policy.
You can reconfigure a specific file transfer service/protocol to use a different security policy, other than the default one, by setting the security_policy = OTHER-SECURITY-UUID option in the service's configuration section.
You can change the configuration options of the default security policy, and it will automatically apply to all file transfer services that don't have an explicit security policy applied.
You can't create a new security policy and assign it as the default security policy. Update the existing default security policy instead.
Security policies lifecycle#
The security policies are automatically started when a file transfer service needs to use them.
You can manually stop a security policy, but it will be automatically started again when a file transfer service needs to use it.
Some configuration changes on the security policies require a restart of the security policy itself, and administrators will have to manually restart the policy. It is not automatically restarted when a file transfer service needs to use it.
Adding a new security policy via Web Manager#
New security policies are added using the Web Manager via the General -> Configuration page.
Adding a new security policy via text configuration#
Adding a new security policy is done by creating a new section inside the configuration file. The name of the section should be prefixed with security-policies/ and followed by the policy's UUID.
The policy's UUID can be any unique string used to identify the policy. Once defined, the UUID should not be changed.
For example, to add a new security policy named Internal Access,
where 78.153.3.0/24 might be the range of VPN users that are not allowed:
[security-policies/a805d3a6-4bbf-abcd-a59b]
name = Internal Access
description = Security policy designed for internal users.
deny_usernames = ftp, admin, administrators
source_ip_filter =
  allow 10.0.0.0/8
  deny 78.153.3.0/24
source_ip_ban_after_count = 10
source_ip_ban_interval = 600
Once the security policy is created you can assign it as the security policy for a specific file transfer service:
[services/1cdff34f-76bc-11f1-a8f3-04cf4b0c43dd]
name = SFTP server
type = sftp
security_policy = a805d3a6-4bbf-abcd-a59b
Source IP filter behavior#
Source IP rules can deny access or exempt matching addresses from the remaining security policy checks. Rules can match an IP address, CIDR range, two-letter country code, or ASN.
A matching deny rule rejects the source address. It is also treated as a blocked source IP during connection checks. For HTTP, source IP rejection can occur at authentication time so that the login page remains available.
A matching allow rule bypasses the policy's remaining source IP ban and username denial checks, including brute force protection configured by source_ip_ban_after_count and source_ip_ban_interval. Basic credential sanity checks still apply. It does not bypass credential verification, account or administrator filters, group or role association, or permission checks.
An empty filter, or a nonempty filter with no match, leaves the remaining security policy checks in effect. There is no implicit final block for security policies.
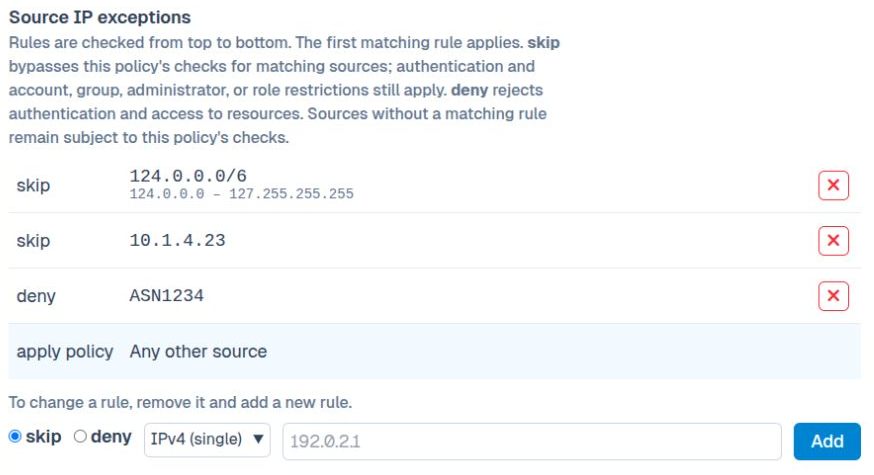
Source IP exceptions in the Web Manager.#
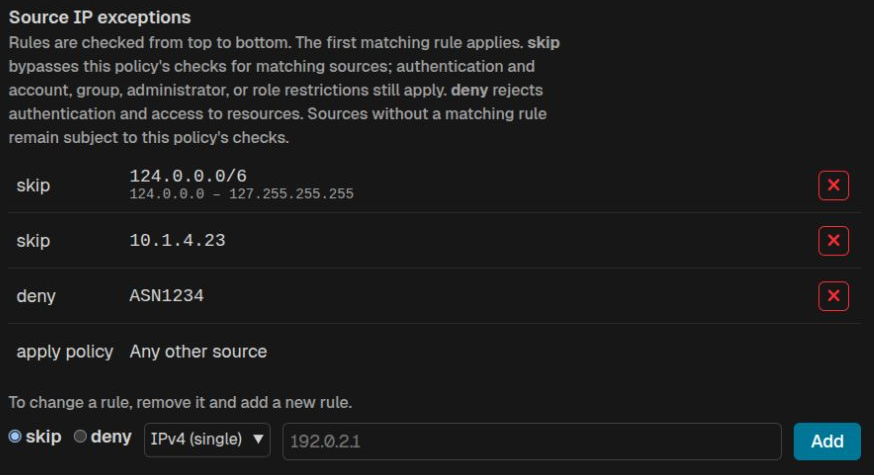
Source IP exceptions in the Web Manager.#
In the Web Manager, allow is labeled skip; deny keeps its name.
For example, to block one network while keeping the normal policy checks for everyone else:
source_ip_filter =
    deny 198.51.100.0/24
To exempt a trusted address from the policy's source IP ban and username denial checks, while continuing normal checks for other addresses:
source_ip_filter =
    allow 192.0.2.23
To allow only a trusted network through this policy, explicit final denial rules are required for both address families:
source_ip_filter =
    allow 192.0.2.0/24
    deny 0.0.0.0/0
    deny ::/0
The allowed network in this last example also bypasses the remaining policy checks described above.
To restrict login addresses while retaining those checks for allowed users, use account and group filters and leave the policy's source IP filter empty.
See source IP filtering for rule syntax, target types, and Web Manager editing.
Below you can find the configuration options available for security policies.
name#
- Default value:
''
- Optional:
No
- From version:
5.15.0
- Values:
Any text.
- Description:
Human-readable short string used to identify this policy.
description#
- Default value:
''
- Optional:
Yes
- From version:
5.15.0
- Values:
Any character string.
- Description:
Human-readable text that describes the purpose of this policy.
deny_usernames#
- Default value:
''
- Optional:
Yes
- Values:
Comma-separated list of usernames.
- From version:
5.15.0
- Description:
Comma-separated list of usernames denied by this policy.
The check is case-insensitive.
Usernames should be defined in lower-case.
Leave empty to not impose any restriction based on the names of users.
This list is not used to deny access to the Web Manager console.
deny_administrators#
- Default value:
''
- Optional:
Yes
- Values:
Comma-separated list of names.
- From version:
5.15.0
- Description:
Comma-separated list of administrator names denied by this policy.
The check is case-insensitive.
Administrator names should be defined in lower-case.
This list is not used to deny access to the file transfer services.
Leave this option empty to allow any username to authenticate as an administrator. In the INI file, an empty value (e.g., deny_administrators =) is treated as an empty list, thus not blocking any administrator.
source_ip_filter#
- Default value:
''
- Optional:
Yes
- Values:
List of rules in action target format, one rule per line.
allow/deny followed by an IP address, CIDR, country, or ASN.
- From version:
5.25.0
- Description:
Defines ordered source IP allow and deny rules for this policy. A matching allow rule bypasses the remaining policy checks; a matching deny rule rejects access. Empty filters and unmatched addresses continue through the other policy checks. Restart the security policy after changing this option.
See source IP filtering for rule syntax, evaluation behavior, and examples.
source_ip_ban_after_count#
- Default value:
5
- Optional:
Yes
- Values:
Number of failed attempts.
- From version:
5.15.0
- Description:
Number of consecutive failed authentications which will result in blocking the source IP.
Set to 0 to disable source IP brute force attack protection.
source_ip_ban_interval#
- Default value:
3600
- Optional:
Yes
- Values:
Number of seconds.
- From version:
5.15.0
- Description:
Number of seconds for which authentication requests from the source IP are denied.
Default interval is 1 hour.
This configuration is ignored when source_ip_ban_after_count = 0.